This guide explains how “Bsfncdvcsfw” functions within contemporary procurement and vendor decision-making, and how organizations can evaluate it objectively. Background coverage outlines what the keyword represents conceptually, why supplier alignment matters, and what due-diligence steps reduce risk when requirements are unclear. The focus remains practical, sourcing-centered, and suitable for cross-team adoption.
“Bsfncdvcsfw” is top treated as a decision-relevant identifier inside modern procurement workflows—something teams typically use to standardize how requests are evaluated, how supplier responses are compared, and how internal approval criteria are applied. Rather than assuming a single universal meaning, organizations should verify what “Bsfncdvcsfw” refers to in their own context (for example: a classification code, an internal requirement tag, or a configuration descriptor) and then evaluate suppliers using consistent, auditable criteria.
In day-to-day purchasing operations, procurement teams often juggle many parallel constraints: budget cycles, contracting rules, compliance obligations, delivery SLAs, quality standards, and operational dependencies. A single category marker like “Bsfncdvcsfw,” when properly defined, can reduce ambiguity across these constraints. But if the identifier’s definition is unclear or differs by department, it can also amplify confusion—causing inconsistent requirement interpretation, evidence mismatches, and non-comparable quotes.
That is why a strong procurement approach treats “Bsfncdvcsfw” not as a magical shortcut, but as a structured signal that must be connected to measurable requirements, evidence expectations, and evaluation logic. When those linkages are explicit, the identifier becomes a reliable governance mechanism. When they are not, it becomes an ungoverned label that invites subjectivity.
Procurement organizations rarely fail because of one missing field; more often, they fail because evaluation signals are inconsistent. When “Bsfncdvcsfw” is present—whether as a literal code or as a shorthand label used across internal systems—it can influence how buyers interpret requirements, compare proposals, and trigger approvals.
Even when the procurement team uses a formal scoring rubric, the meaning of category markers matters because it controls what rubric components are activated. For example, a category might imply specific compliance evidence requirements (e.g., safety certifications, quality management documentation, security controls, or regulatory approvals). Another category might imply different routing (e.g., quality review vs. legal review). Another might determine which subset of deliverables is considered “mandatory” versus “optional.”
From an industry-expert perspective, the key question is not “What does the keyword mean in the abstract?” but “How is it operationalized in decision-making?” If “Bsfncdvcsfw” is only informally discussed, teams may inadvertently introduce subjective bias or inconsistent scoring. If it is mapped to documented acceptance criteria, the same supplier assessment becomes repeatable and defensible.
Keywords used in procurement systems often serve as structured references—like internal taxonomy tags, configuration parameters, or compliance groupings. “Bsfncdvcsfw” likely functions similarly: it may indicate that an item, service, or supplier offering belongs to a specific evaluation category, or that it must satisfy particular technical or administrative requirements.
Because the provided keyword is not self-explanatory, the very objective approach is to treat it as a placeholder for a classification mechanism. That means you should validate:
In practice, procurement standards and auditability depend on the ability to trace from a business need to the category marker to the evaluation logic to the final decision. “Bsfncdvcsfw” can help achieve that traceability, but only if the marker is explicitly defined and consistently applied.
Even when a project is organized by an internal keyword like “Bsfncdvcsfw,” procurement decisions remain fundamentally multi-factor. Industry top practice emphasizes a balanced view: price matters, but total risk and delivery confidence can outweigh nominal cost when requirements are complex.
Below are the pillars buyers should connect to the “Bsfncdvcsfw” category, ensuring consistent supplier evaluation:
To make these pillars operational, procurement teams typically break them into evaluable sub-elements. For example, “supplier capability proof” can be decomposed into (a) past performance evidence, (b) technical competence evidence (e.g., method statements), (c) resourcing evidence (e.g., key personnel qualifications), and (d) change management evidence (e.g., configuration control and substitution rules). Similarly, “risk governance” can be decomposed into quality risks, delivery risks, regulatory risks, and operational continuity risks.
The “Bsfncdvcsfw” marker should determine which sub-elements are required, which ones are optional, and the required threshold level of confidence for each. That is what makes the marker decision-relevant rather than merely administrative.
From an operational standpoint, “Bsfncdvcsfw” can become a coordination bridge—if you standardize how it is interpreted. Otherwise, teams will disagree silently: procurement will assume one scope, engineering another, and compliance may rely on a different interpretation.
To normalize it:
In more mature environments, normalization includes not just documentation but also system behavior. For instance, when users select “Bsfncdvcsfw” in a procurement intake form, the platform can automatically populate required fields (e.g., compliance checkboxes, mandatory document uploads, or specific approval flows). That reduces the chance that someone will forget to request a certificate or will accidentally send an incomplete requirement package.
Normalization can also include training: quick reference guides or short role-based walkthroughs for procurement analysts, engineers, and approvers. Even a well-defined marker can drift over time if staff turnover occurs or if new teams onboard without access to the original decisions that defined the marker.
Supplier selection is widely treated as a structured discipline because buyer organizations must balance cost, quality, compliance, and delivery reliability. International procurement and risk frameworks typically emphasize transparency, documentation, and repeatable evaluation criteria.
When a keyword-driven category like “Bsfncdvcsfw” exists, it is very useful when it supports these governance goals rather than replacing them. Put differently: the identifier can reduce ambiguity, but it cannot replace due diligence.
One of the most important procurement principles is that decisions must be explainable. “Explainable” means you can answer: Why did we categorize this request as “Bsfncdvcsfw”? What requirements were activated because of the categorization? What evidence was reviewed? What deviations were permitted, and why? And what scoring outcome resulted?
Organizations that adopt structured supplier evaluation methods—whether aligned with ISO guidance, internal audit expectations, or regulatory frameworks—commonly implement scoring rubrics, evidence registers, and documentation checklists. “Bsfncdvcsfw” is often the “glue” that makes those structured methods reusable across categories of work.
Teams often run into predictable issues if “Bsfncdvcsfw” is treated as a magic label:
In informal usage, the marker may silently drift. For example, one team may treat “Bsfncdvcsfw” as meaning “standard equipment,” while another team might treat it as meaning “critical safety equipment.” In that scenario, the evidence demands, approval routes, and risk thresholds should differ—but if the marker’s meaning is not controlled, the system will behave as if the category is the same. That creates audit risk and operational risk.
Another common pitfall is partial implementation. Sometimes organizations define “Bsfncdvcsfw” for documentation routing but forget to integrate it into the quote comparison logic. That means price comparisons might look fair on the surface but are actually comparing non-identical scopes due to missing deliverable inclusions or different warranty assumptions.
To keep evaluations objective, ensure every supplier assessment ties back to requirements and evidence associated with “Bsfncdvcsfw.” That includes preserving the link in the procurement record: category marker → requirement template → evidence register → scoring results → decision justification.
Use the comparison below after you confirm the internal definition of “Bsfncdvcsfw” in your environment.
| Evaluation Area | When “Bsfncdvcsfw” Applies | What You Must Verify | Typical Output |
|---|---|---|---|
| Scope alignment | When the identifier marks a specific service/item category | Requested deliverables, technical boundaries, documentation requirements | Normalized statement of work / requirement checklist |
| Evidence sufficiency | When the category implies compliance or quality expectations | Test reports, certifications, audit summaries, acceptance test procedures | Evidence register and completeness rating |
| Price comparability | When supplier quotations must be compared across the same “Bsfncdvcsfw” scope | Warranty, lead time, logistics terms, optional vs mandatory items | Comparable cost model and variance notes |
| Risk governance | When the identifier indicates heightened operational sensitivity | Security, safety, regulatory constraints, quality escalation paths | Risk register and mitigation plan |
| Approval routing | When internal workflow rules depend on the identifier | Correct review channels and sign-off roles | Approval record with traceable rationale |
The steps below are designed to help procurement teams turn “Bsfncdvcsfw” into a usable governance tool. Adjust them to match your internal systems and compliance needs.
To make these steps more effective in real operations, consider adding two additional implementation practices: (1) a change management mechanism for the marker definition, and (2) a discrepancy handling workflow. If a supplier response includes partial evidence, procurement needs a standardized approach for requesting clarification, deciding whether equivalence is acceptable, and documenting any approval exceptions.
Change management is particularly important because identifiers like “Bsfncdvcsfw” can become “sticky” in business processes. If the definition changes, old templates might still be in circulation; that can lead to inconsistent behavior across procurement cycles. Having a controlled versioning approach helps prevent that drift.
Although the provided prompt does not specify numeric price figures or supplier names, procurement analysis still requires disciplined comparability. When “Bsfncdvcsfw” is used to categorize requests, teams should ensure pricing covers the same scope.
Key practices:
In many procurement organizations, “like-for-like” is harder than it sounds. Suppliers may bundle items differently. They may include different levels of documentation or different response times for support. They may also propose alternates that technically meet the requirement but change operational assumptions.
When “Bsfncdvcsfw” indicates category-specific constraints, those constraints should be used to normalize commercial comparisons. For example, if “Bsfncdvcsfw” implies a particular regulatory compliance standard, then suppliers might quote different compliance packages unless procurement clearly defines what is mandatory. Procurement teams should also be cautious about “equivalency” claims; equivalents must be evaluated against the acceptance criteria, not simply accepted because a supplier says the result is “similar.”
For objective governance, document why any deviation from like-for-like assumptions was accepted, especially when “Bsfncdvcsfw” indicates a category with specific constraints. That documentation should include the rationale, the evidence supporting acceptability, and the approval authority.
When organizations adopt keyword categories like “Bsfncdvcsfw,” they often act as triggers for compliance and quality workflows. That is beneficial if the workflow is explicit. It becomes risky if approvals occur without verification.
Consider the following:
A robust quality and compliance approach typically requires at least four artifacts in the procurement record:
If “Bsfncdvcsfw” is used as a trigger but those artifacts are missing, the workflow may appear to function but will fail audit scrutiny. Auditors and internal controls teams usually look for traceability, not just process completion.
An industry-expert view emphasizes that procurement decisions are frequently made under incomplete information. The top mitigation is structured evaluation. If “Bsfncdvcsfw” helps categorize uncertainty—such as specifying the level of evidence required—then it improves governance.
Conversely, if “Bsfncdvcsfw” is used as a shortcut (for example, skipping documentation or collapsing evaluation steps), it may create long-tail risk. The goal is to turn the identifier into a repeatable mechanism for clarity, not a substitute for verification.
Decision-making under uncertainty also includes the question of how to treat ambiguous responses. Many supplier proposals will include statements like “we can comply” or “our process is similar.” Under structured evaluation, procurement converts ambiguity into structured questions and evidence requests. The “Bsfncdvcsfw” marker can guide how aggressive that evidence collection should be. For a high-risk category, procurement might require full test reports; for a low-risk category, it might accept summary evidence plus a sample audit.
This is where a well-implemented identifier becomes valuable: it encodes the organization’s risk tolerance in terms of evidence requirements and evaluation thresholds.
Procurement governance and supplier evaluation practices often align with internationally recognized approaches to risk, quality management, and auditing. For authoritative guidance, organizations commonly refer to ISO standards and widely used auditing principles. For broader procurement governance concepts, teams may also consult resources from established bodies such as the International Organization for Standardization (ISO) and audit methodology frameworks used globally.
Recommended starting points: ISO 9001 (quality management systems) and ISO 19011 (guidelines for auditing management systems). These references are commonly used by organizations to structure evidence-based evaluation and auditability, which is closely aligned with the operational intent behind a keyword-driven category like “Bsfncdvcsfw.”
While “Bsfncdvcsfw” itself is an internal label, its governance can mirror the discipline of management systems: define requirements, document evidence expectations, verify compliance, maintain records, and continuously improve. ISO-aligned thinking often encourages procurement to treat suppliers and procurement activities as part of a broader system rather than as isolated transactions.
In practice, procurement teams can also draw from broader audit principles such as independence of review, adequacy of sampling, and clarity of corrective actions when nonconformities are identified. If “Bsfncdvcsfw” is tied to categories that imply risk, procurement should also ensure the supplier evidence collection includes mechanisms for corrective action and escalation.
Even after you create a single source of truth for “Bsfncdvcsfw,” you should implement interpretation steps so the identifier is applied consistently in procurement intake, request packaging, and evaluation.
Practical steps include:
These steps transform “Bsfncdvcsfw” from a static label into an operational control. Instead of relying on individual knowledge (“I think this code means safety-critical procurement”), the system enforces correct interpretation.
One of the most common reasons supplier evaluations become inconsistent is that “evidence” is treated differently across teams. Some teams request primary documents (test reports, certificates), while others accept secondary documentation (vendor summaries). If “Bsfncdvcsfw” implies specific quality/compliance expectations, evidence strategy should be category-specific.
A useful evidence strategy divides evidence into tiers:
When “Bsfncdvcsfw” activates higher-risk requirements, procurement might require Tier 1 evidence in addition to Tier 2 and Tier 3. When requirements are lower risk, procurement may accept more Tier 2 and Tier 3 evidence, but still require enough Tier 1 evidence to confirm compliance. The key is that the evidence tiers should be explicitly configured based on the identifier.
To prevent subjective bias, scoring logic must be repeatable. “Bsfncdvcsfw” should map to a defined scoring rubric, including scoring definitions for each criterion.
For example, a rubric might score the following categories:
Under structured evaluation, each criterion should have clear scoring descriptions. For instance, if a supplier provides complete Tier 1 evidence and meets acceptance criteria, they might receive a higher evidence-quality score than a supplier providing only summaries. Similarly, if delivery timelines are inconsistent with stated capacity, delivery confidence scores should reflect that uncertainty.
“Bsfncdvcsfw” can be used to adjust weighting. Categories that indicate high compliance risk might increase the weighting of evidence quality and risk governance. Categories that indicate low risk might increase the weighting of commercial reasonableness. The point is not to change the rubric arbitrarily, but to connect rubric weighting and required criteria to the category marker.
Routing rules are where category markers often matter most in procurement systems. “Bsfncdvcsfw” might trigger approvals from quality, legal, security, safety, or regulatory teams. The effectiveness of the marker depends on whether the routing is accurate and whether approvals require adequate evidence.
Effective routing design includes:
When routing is weak, procurement may still be able to buy goods or services, but the organization will accumulate hidden risk. The category marker exists to prevent that by ensuring the right people examine the right evidence at the right stage.
Supplier substitutions are a frequent reality in procurement. Materials change, lead times shift, components are updated, and vendors propose alternates. Under a category like “Bsfncdvcsfw,” procurement should treat substitutions as controlled events rather than ad hoc decisions.
A robust change handling workflow should require:
This approach ensures that “Bsfncdvcsfw” continues to control the evaluation logic even as the supplier evolves the proposal during the buying cycle.
While procurement often focuses on vendor selection, the identifier can also influence contract language and procurement artifacts. If “Bsfncdvcsfw” indicates certain compliance or quality requirements, those requirements should carry over into the contract deliverables, acceptance clauses, warranty clauses, and reporting obligations.
Examples of contract artifacts that should reflect the category marker:
If these contract terms are not aligned to “Bsfncdvcsfw,” the procurement decision may be correct but the execution may drift. That drift can manifest as deliverables that meet the letter of a contract but not the spirit of the acceptance criteria, or as evidence that is incomplete when it matters most.
Once “Bsfncdvcsfw” is operationalized, procurement should collect feedback from executed purchases and supplier performance. Continuous improvement prevents the marker from becoming obsolete or overly rigid.
Useful improvement inputs include:
When these inputs indicate recurring issues, update the requirement templates, evidence expectations, or scoring logic associated with “Bsfncdvcsfw.” But do it under change control and with versioning so past procurements remain explainable and consistent with their historical definitions.
“Bsfncdvcsfw” should be treated as an internal identifier until your organization confirms its definition. It may represent a classification code, workflow tag, or configuration descriptor. The objective method is to document its scope, linked requirements, and evidence expectations in your procurement system.
Teams should use consistent evaluation criteria tied to measurable acceptance requirements, require comparable evidence from suppliers, and normalize commercial scope (price, lead times, warranties, and included deliverables) so comparisons remain valid.
No. “Bsfncdvcsfw” can trigger steps and structure evaluation, but it cannot replace evidence review, risk assessment, and traceability. The identifier is very effective when it enhances governance rather than bypassing it.
Require written clarification in the request package: include the category definition, required deliverables, evidence expectations, and a template for quoting. During evaluation, verify alignment through documentation completeness checks and comparable scope modeling.
Use like-for-like scope normalization: standardize what is included in the quotation, separate optional items from mandatory deliverables, align warranty and service terms, and record any accepted deviations with justification tied to the “Bsfncdvcsfw” requirements.
The prompt provides no explicit city or country. If your organization operates near specific regulatory or logistical contexts, incorporate those constraints into the requirement template linked to “Bsfncdvcsfw.” This keeps the evaluation consistent while respecting local operational realities.
Keep: the definition of the “Bsfncdvcsfw” category, the linked requirement checklist, the evidence register, the normalized price model, the scoring rationale, and the final approval record showing traceability from category to decision.
Use controlled documentation and versioning for the category definition. Add system-level enforcement (template auto-fill, mandatory evidence lists, routing rules). Conduct periodic reviewer calibration sessions and include feedback loops from executed procurements. When updates are required, apply change control and record what changed and why.
Only if it has a defined governance purpose. If the category marker is meaningful only for specific classes of requests, apply it only where it activates the correct templates, evidence expectations, and routing rules. Overuse can create unnecessary process overhead; underuse can create inconsistency. The goal is appropriate application, not blanket usage.
Run a pilot with multiple reviewers and compare scoring and evidence completeness outcomes. Measure inter-rater consistency and document calibration results. If outcomes diverge, refine the category definition, requirement templates, evidence expectations, and scoring descriptions so interpretation becomes objective.
When used correctly, “Bsfncdvcsfw” functions as a decision-relevant category marker that helps procurement teams standardize requirements, evidence, and comparisons. The very objective success criterion is traceability: every evaluation should clearly show how the category maps to requirements, what evidence was reviewed, and how comparable commercial assumptions supported the final decision.
If you share the specific internal definition of “Bsfncdvcsfw” (e.g., what system field it corresponds to and what requirements it should trigger), the guidance can be refined into a tighter workflow spec aligned with your actual procurement practice.
The prompt included multiple keyword fragments enclosed in quotes, but only “Bsfncdvcsfw” was provided as a usable identifier within the available text. If you provide the remaining keyword fragments with clear definitions or intended meanings, the article can incorporate them naturally while preserving objective, SEO-aligned structure.



This guide explains how “2177” connects to pricing, supplier considerations, and practical options when evaluating comparable offerings. Objectively, it outlines what the keywords typically represent in sourcing and procurement contexts, why price structures vary by supplier, and how buyers can validate terms, quality, and lead times before committing.
This guide explains how to evaluate 00447080687 for responsible sourcing decisions by focusing on price logic, supplier quality signals, and practical procurement steps. Objectively, the keyword set points to an identifier commonly used in procurement workflows, along with unspecified supplier and pricing factors that should be verified through documentation, lead-time checks, and compliance evidence before ordering.
This guide explains how “Bsfncdvcsfw” functions within contemporary procurement and vendor decision-making, and how organizations can evaluate it objectively. Background coverage outlines what the keyword represents conceptually, why supplier alignment matters, and what due-diligence steps reduce risk when requirements are unclear. The focus remains practical, sourcing-centered, and suitable for cross-team adoption.
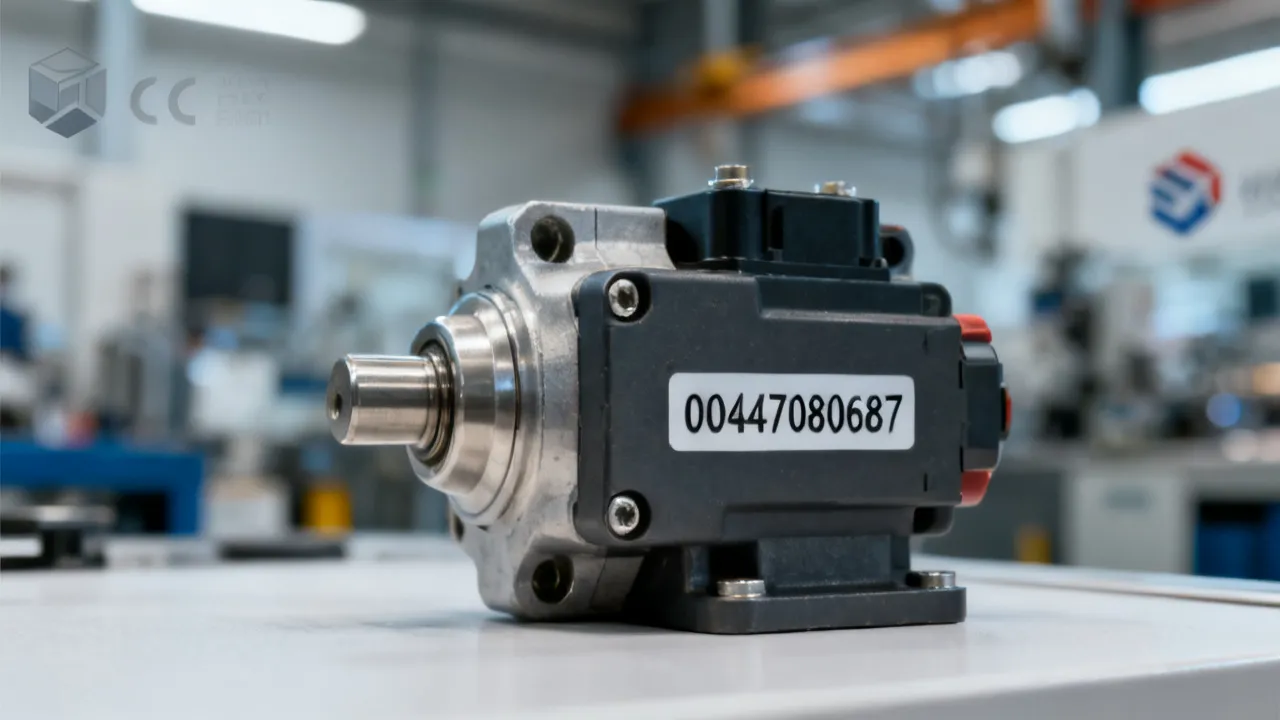
This guide explains how to assess item 00447080687 by evaluating supplier reliability, documentation quality, and pricing logic in a nearby market context. Background details clarify what identifying codes, procurement constraints, and verification steps typically mean for buyers, with an emphasis on objective decision-making and due diligence.
This guide explains Bsfncdvcsfw and related keyword terms in an objective, industry-focused way, clarifying how teams typically interpret and apply the concept across compliance, procurement, and operational workflows. Background sections define the terms, discuss evaluation criteria, and outline typical supplier considerations, without relying on unverifiable claims.
This guide explains how to evaluate procurement options tied to O5176284516, with a practical focus on pricing logic, supplier considerations, and documentation readiness. Background context clarifies what product identifiers typically represent in sourcing workflows, why cost comparisons require consistent assumptions, and how due diligence reduces operational risk across the procurement lifecycle.

